44 palo alto antivirus inspection
Palo Alto SaaS Security and Its Benefits as a Next-Gen CASB Service Initially, the issue isn't spotted until real-time inspection policies are enabled, and a lag and lower performance are introduced. IT departments also need to ensure that users aren't deploying unsanctioned SaaS applications (the so-called Shadow IT). Even non-web SaaS applications should be inspected. For all this, a CASB solution is required. Palo Alto Networks Approach to Intrusion Prevention In 2020, AV-TEST test identified over 1.1 billion malware samples, with 2021 already surpassing that amount.1 Palo Alto Networks threat intelligence team, Unit 42, monitored a total of 4,120 newly released severe vulnerabilities between May 2021 and July 2021, as well as a total of 2.29 million malicious sessions.
Threat Prevention Datasheet - Palo Alto Networks Threat Prevention protects your network against these threats by providing multiple layers of prevention, confronting threats at each phase of the attack. In addition to traditional intrusion-prevention capabilities, we provide the unique ability to detect and block threats on any and all ports, instead of invoking signatures based on a limited ...

Palo alto antivirus inspection
Check Point vs Palo Alto: Compare EDR software - TechRepublic Unknown files are examined by WildFire inspection and analysis. WildFire uses dynamic, static and bare-metal analysis to provide thorough and evasion-resistant threat identification. It scans and... Tips & Tricks: Enable Packet Captures on Security Profiles | Palo Alto ... The range is 1-50 and the default is 5. To view the packet capture, navigate to Monitor > Logs > Threat and locate the log entry you are interested in and then click the green down arrow in the second column. Packet captures will only occur if the action is allow or alert, and the green arrow is only shown when a packet capture has been obtained. How to Segment the Data Center - Palo Alto Networks All allowed data center communication should traverse a firewall and undergo full threat inspection (antivirus, anti-spyware, vulnerability protection, file blocking, WildFire analysis, and URL Filtering for data center traffic that leaves the enterprise and for applications hosted by customer tenants).
Palo alto antivirus inspection. Security Profile: Anti-Spyware - Palo Alto Networks —For each threat signature and Anti-Spyware signature that is defined by Palo Alto Networks, a default action is specified internally. Typically the default action is an alert or a reset-both. The default action is displayed in parenthesis, for example default (alert) in the threat or Antivirus signature. Allow —Permits the application traffic The Product Summary Specsheet - Palo Alto Networks Nov 23, 2021 at 12:00 AM. Share. Key features, performance capacities and specifications for all Palo Alto Networks firewalls. This specsheet is also available in: Fortinet vs Palo Alto | EDR Software Comparison - TechRepublic Palo Alto can then send unidentified files to WildFire for deeper inspection and analysis to quickly expose potential malware. The Cortex XDR agent also leverages a behavioral threat detection... Configuration Wizard Release Notes - LIVEcommunity about configuration wizard the palo alto networks ⓡ configuration wizard guides customers step-by-step by providing an intuitive, easy-to-use interface to configure firewalls that aligns with best practices.configuration wizard provides customized recommendations to remediate bpa-found issues and improve overall feature adoption and improve …
Security Assurance - Palo Alto Networks The first step toward Security Assurance is to run the Best Practice Assessment (BPA) to measure your adoption of seven key security capabilities: WildFire, Antivirus, Anti-Spyware, DNS Sinkhole, URL Filtering, Vulnerability Protection, and Logging. We recommend that you ensure your adoption rate for those security capabilities is at least ... Threat Assessment: BlackByte Ransomware - Unit42 BlackByte is a RaaS that leverages double extortion as part of attacks. The threat actors behind the ransomware deploy a name-and-shame approach to victim shaming, as they operate a Tor .onion auction site where they sell stolen victim data. The operators even go so far as to link the auction site in the ransom note to scare victims. A Few Amazing Things About Palo Alto Firewall PA-400 Series These advanced security NGFWs by Palo Alto offer a low total cost of ownership (TCO) and easy deployment with automatic configuration in small spaces and remote locations due to their compact desktop form factor. These features enable zero-trust network security, allowing organizations and employees to operate from anywhere. Palo Alto Networks Next-Generation Firewalls - TrustRadius User Review of Next-Generation Firewalls - PA Series: 'We have deployed Palo Alto Networks Next-Generation Firewalls - PA Series in our Head office in High availability mode. This Palo Alto Networks Next-Generation Firewalls - PA Series is deployed on the internet gateway/perimeter to filter only good traffic and around 300 users and 30-35 servers are connected behind this firewall. Also, this ...
Content and Threat Detection State - Palo Alto Networks Collects information about the device's Content and Threat Detection (CTD) engine state. This information includes version information, including the latest version of threat, app, virus, WildFire, and WildFire Public Cloud that is in use by the device. Also include engine configuration status such as whether the bloom filter is in use, query ... Russia Hackers Abusing BRc4 Red Team Penetration Tool in Recent Attacks According to Palo Alto Networks' researchers, someone uploaded a document to the VirusTotal website for inspection in May 2022. This document included a BRc4-associated payload. Surprisingly, 56 of VirusTotal scanners couldn't recognize the malware, after which it was assigned Benign status. Possible Perpetrator? LockBit 2.0: How This RaaS Operates and How to Protect Against It Palo Alto Networks customers receive protections against LockBit 2.0 attacks from Cortex XDR, as well as from the WildFire cloud-delivered security subscription for the Next-Generation Firewall. ... Ensure 'SSL Inbound Inspection' is required for all untrusted traffic destined for servers using SSL or TLS: ... Ensure that antivirus profiles are ... Configuration Wizard Release Notes Version 1.3.0 - Palo Alto Networks The Palo Alto NetworksⓇ Configuration Wizard guides customers step-by-step by providing an intuitive, easy-to-use interface to configure firewalls that aligns with best practices. Configuration Wizard provides customized recommendations to remediate BPA-found issues and improve overall feature adoption and improve security posture.
Mastering Palo Alto Networks - FREE DOWNLOAD IM & SEO TOOLS, WSO ...
10 Best EDR Security Services In 2022 for Endpoint Protection #1) Cynet - Recommended EDR Security Service #2) ManageEngine Desktop Central #3) CrowdStrike #4) Carbon Black #5) SentinelOne #6) Symantec EDR #7) Cybereason #8) Palo Alto Networks XDR #9) Cisco AMP #10) FireEye HX #11) McAfee EDR Conclusion Recommended Reading List of Top EDR Security Services

Digital: Palo Alto Networks’ Unit 42 Researchers Share Study On How ...
The Best Firewalls for Small Businesses in 2022 | Business.org One thing to keep in mind, though, is Palo Alto firewalls use only stateful packet inspections (at least as far as we can tell). That means the firewall doesn't analyze the actual data transmitted to your device—just basic info like the origin IP address. That makes it a bit less effective than some of the other options on our list.

Palo Alto | IP ON WIRE
Threat Assessment: BlackCat Ransomware - Unit42 Palo Alto Networks detects and prevents BlackCat ransomware with the following products and services: Cortex XDR and Next-Generation Firewalls (including cloud-delivered security subscriptions such as WildFire). Due to the surge of this malicious activity, we've created this threat assessment for overall awareness.

2 Palo Alto students sent home due to potential coronavirus exposure ...
LIVEcommunity - Best Practice Assessment Plus ... - Palo Alto Networks The WildFire Cloud and on-premises private cloud analyzes new files that the firewall hasn't seen before. It sends all new files for all applications to WildFire for analysis and inspection. WildFire detects unknown threats in all file types and protects you against zero-day threats (new malware) and advanced persistent threats.
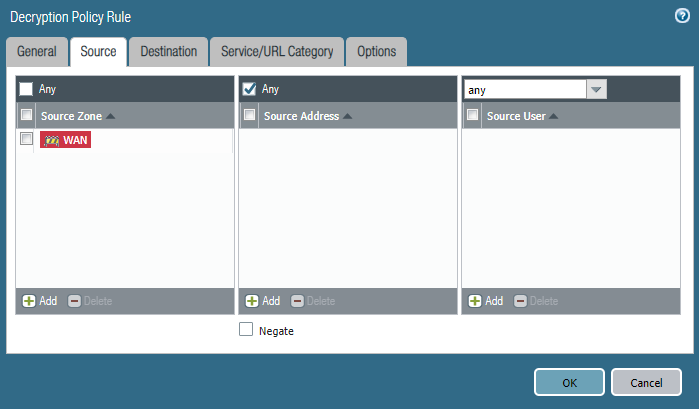
Palo Alto – SSL Inbound Inspection Webserver – Faatech
VM-Series Virtual Firewalls | Prisma - Palo Alto Networks Go beyond simple port blocking with integrated security services. Inspect every inbound/outbound packet for known/unknown threats. Stop outbound traffic exfiltration Integrated DLP blocks attackers from accessing and removing sensitive data. Leverage traffic decryption for outbound inspection. Get cloud-level flexibility and agility

HTTP/2 Inspection | Palo Alto Networks
FQDN Refresh Time | Palo Alto Networks On our Palo Altos (managed with Panorama) in the GUI the Minimum FQDN Refresh Time (sec) is set to 30 seconds. And the FQDN Stale Entry Timeout (min) is set to 1440 mins. But in the CLI FQDN refresh value countdown is starting at 1199 seconds (20 mins) and that is what I also can see in the real world.

19.1 Security Profiles.pdf - Security Profiles o o o o o o o Palo Alto ...
Configuration Wizard Release Notes Version 1.4.0 - Palo Alto Networks The Palo Alto NetworksⓇ Configuration Wizard guides customers step-by-step by providing an intuitive, easy-to-use interface to configure firewalls that aligns with best practices.Configuration Wizard provides customized recommendations to remediate BPA-found issues and improve overall feature adoption and improve security posture.

PPT - Palo Alto Networks PCNSE6 Actual Exam Question Answers PowerPoint ...
Cisco ASA Firewall Vs Palo Alto Firewall! (Table Comparison) Palo Alto's PA-5220 firewall was determined to be more cost-effective than Cisco's, with a total cost of ownership (TCO) per protected Mbps of $7 compared to $28 for the Cisco Firepower 4120 in recent NSS Labs testing. The Cisco Firepower's failure to block three of the 190 evasion tactics assessed by NSS contributed to the low ranking.
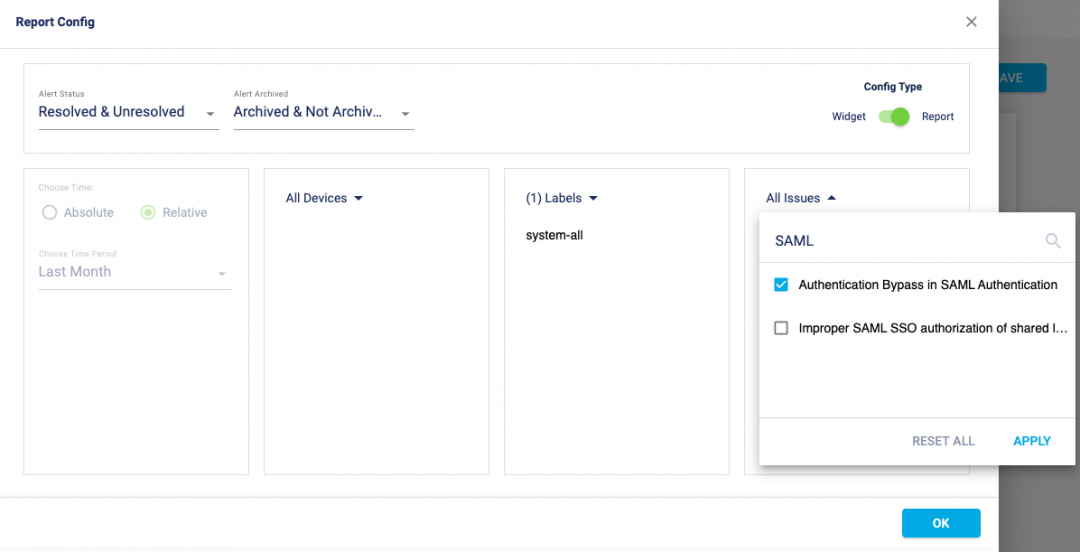
Patch is available for the Critical Vulnerability (CVE-2020-2021 ...
Security Profile: Antivirus - docs.paloaltonetworks.com Antivirus profiles protect against viruses, worms, and trojans as well as spyware downloads. Using a stream-based malware prevention engine, which inspects traffic the moment the first packet is received, the Palo Alto Networks antivirus solution can provide protection for clients without significantly impacting the performance.

MendWorx - IT Solutions and Services
Changelogs for CIS Palo Alto Firewall 6 Benchmark L1 v1.0.0 6.1 Ensure at least one antivirus profile is set to block on all decoders except 'imap' and 'pop3'. 6.10 Ensure that URL Filtering uses the action of 'block' or 'override' on the URL categories. 6.11 Ensure that access to every URL is logged. 6.12 Ensure all HTTP Header Logging options are enabled - Log Container Page.

Palo Alto Networks - Networking & VPN Connectivity - NextGig Systems ...
Best Intrusion Detection and Prevention Systems (IDPS) for 2022 High availability with watchdog timers, built-in inspection bypass, and hot swaps Out-of-the-box recommended settings for configuring threat protection policies Deep pack inspection and...
final inspection - City of Palo Alto | Manualzz
How to Segment the Data Center - Palo Alto Networks All allowed data center communication should traverse a firewall and undergo full threat inspection (antivirus, anti-spyware, vulnerability protection, file blocking, WildFire analysis, and URL Filtering for data center traffic that leaves the enterprise and for applications hosted by customer tenants).

Dynamic Updates - Antivirus | Palo Alto Networks
Tips & Tricks: Enable Packet Captures on Security Profiles | Palo Alto ... The range is 1-50 and the default is 5. To view the packet capture, navigate to Monitor > Logs > Threat and locate the log entry you are interested in and then click the green down arrow in the second column. Packet captures will only occur if the action is allow or alert, and the green arrow is only shown when a packet capture has been obtained.

Palo Alto declares coronavirus 'state of emergency' | News | Palo Alto ...
Check Point vs Palo Alto: Compare EDR software - TechRepublic Unknown files are examined by WildFire inspection and analysis. WildFire uses dynamic, static and bare-metal analysis to provide thorough and evasion-resistant threat identification. It scans and...
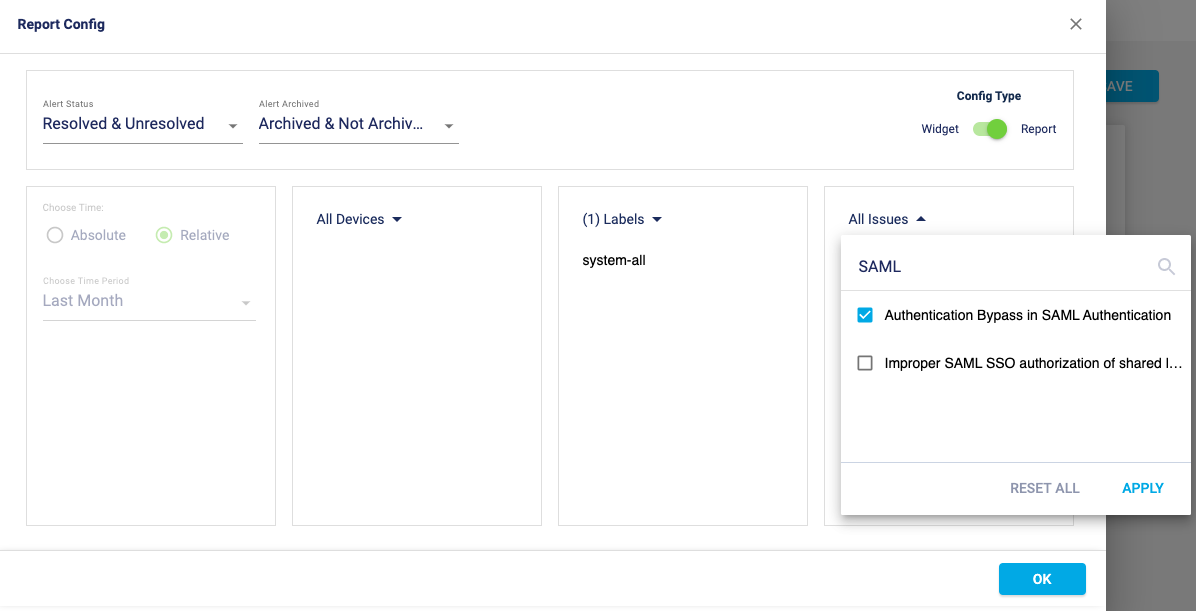
Patch is available for the Critical Vulnerability (CVE-2020-2021 ...

Palo Alto Networks PA-5020 | Palo Alto Networks

Palo Alto firewall Architecture Overview | IP ON WIRE

Home | City of Palo Alto
0 Response to "44 palo alto antivirus inspection"
Post a Comment